Trust Centre
Trust is earned, not declared
As a unified governance platform, we hold ourselves to the same standards across every domain we help you govern. Transparency is our foundation.
- Multi-tenant isolation
- TLS 1.3 + AES-256 encryption
- EU data residency
- SSO & MFA enforced
- Data protection by design
- Security by design
- Responsible AI built in
- Risk-managed operations
Our trust pillars
Foundational commitments that guide how we build, operate, and evolve our platform.
Our commitment to data protection and privacy by design
Enterprise-grade security embedded throughout our platform
Clear information about service health and availability
Aligned with international standards and frameworks
Human-centric AI with transparency and oversight
Integrity, accountability, and ethical business practices
Certifications & compliance
We're committed to achieving and maintaining industry-recognized certifications. Here's our current status and roadmap.
ISO/IEC 27001
Information security management system
Target: 2026
SOC 2 Type II
Security, availability and confidentiality controls
Target: 2027
ISO 27701
Privacy information management system
Target: 2027
GDPR compliance
EU General Data Protection Regulation
Our commitment to transparency
We believe in being honest about where we are on our certification journey. As a governance platform, we understand the importance of these standards and are actively working toward achieving them. We'll update this page as we progress.
Platform security
Security is embedded throughout our platform, from architecture to operations. We use the same governance tools we build to manage our own security posture.
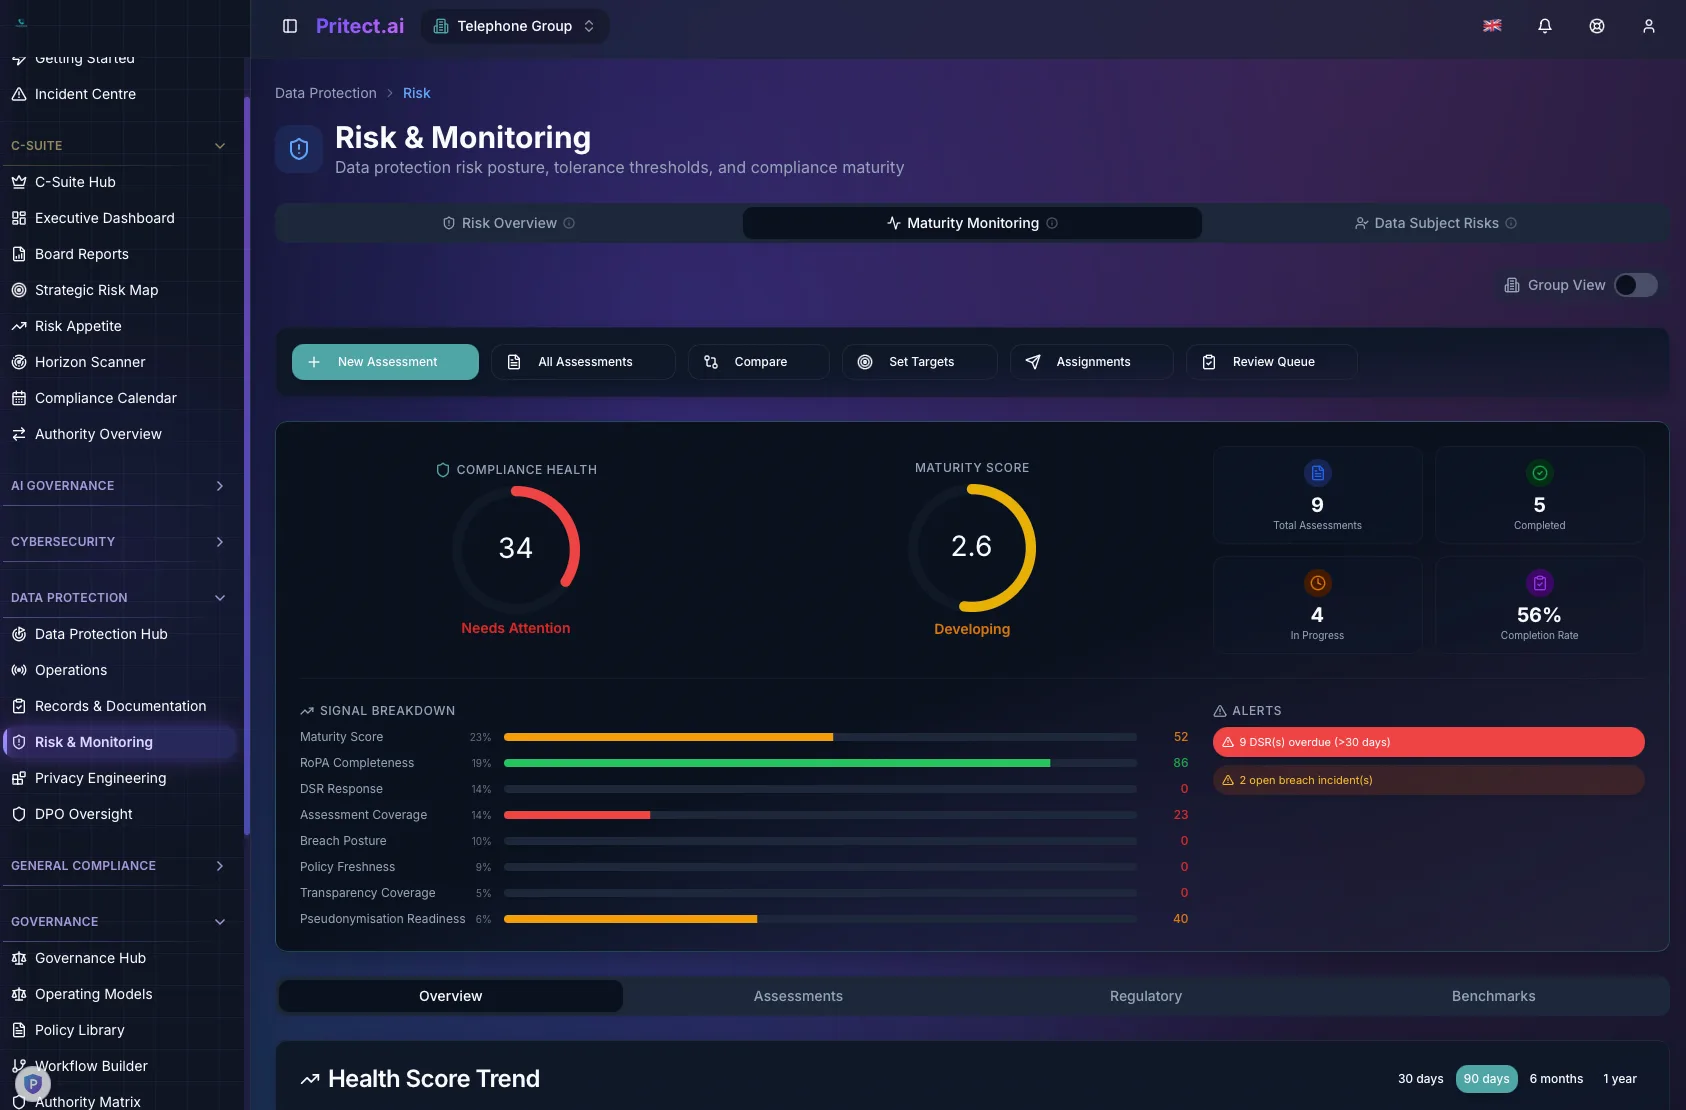
Pritect's maturity assessment framework, the same tools we use internally to track our security posture
Multi-tenant architecture
Complete tenant isolation enforced by the database itself: row-level security on every tenant table, with cross-tenant access denied by design.
Encryption standards
TLS 1.3 for data in transit, AES-256 for data at rest. All sensitive fields encrypted at the application level.
Role-based access control
Granular RBAC with platform, tenant, module, and entity-level permissions. Custom roles supported.
Authentication and SSO
Enterprise SSO over SAML 2.0 with Okta, Microsoft Entra ID, Google Workspace or any other SAML 2.0 identity provider. MFA with step-up enforcement, available on every account by policy.
Comprehensive audit logging
Every action logged with user, timestamp, and context. Audit logs retained for compliance periods.
Secure infrastructure
Hosted on enterprise-grade cloud infrastructure with DDoS protection, WAF, and automatic scaling.
Continuous monitoring
Continuous automated monitoring with threat detection, alerting, and regular vulnerability scanning.
Incident response
Documented incident response procedures with defined SLAs, run on the same Incident Centre we ship to customers.
Service status and availability
For the latest information we have about Pritect's availability, use our public status page. It shows the results of configured monitors and any service updates we have published.
Public status page
Check the current reported status
Conditions can change quickly, so we do not reproduce a status snapshot here. Open the status page for the most recent monitor results and published notices.
Current monitor results
The latest reported state for the services monitored on the status page.
Recent history
Recorded uptime history for each listed monitor, where data is available.
Incident updates
Updates we publish while investigating and resolving a service incident.
Planned maintenance
Notices for scheduled work that may affect service availability.
The status page reflects the monitors and notices currently configured. It may not identify every customer-specific issue or show a newly developing incident immediately. If your experience differs from the reported status, please contact support.
Responsible AI
AI Governance You Can Verify
Pritect embeds the same governance rigour in its own AI that it helps organisations implement. Every AI feature is designed around transparency, human oversight, and data sovereignty, backed by documented controls, not just promises.
Powered by Mistral, European AI
Pritect's AI features are powered by Mistral, a leading European AI company headquartered in Paris. Mistral is included in the platform and serves every organisation by default, so AI processing aligns with EU data sovereignty principles, GDPR expectations, and the values of organisations operating in regulated environments. Pritect's contract with Mistral includes a training opt-out and Zero Data Retention, so Mistral neither retains your data nor uses it for model training. That is a statement about the model provider: AI outputs Pritect saves, such as Speak Up triage drafts, translated summaries and voice transcripts, are stored in your tenant until deleted under its retention schedule.
Organisations on an enterprise plan that prefer a different AI provider may select one, currently Mistral, OpenAI, Anthropic or Google, using their own API key and their own agreement with that provider. The choice applies to the chat-based AI features and to the whole organisation. A provider the organisation configures is its own processor, not a Pritect sub-processor, and the organisation is responsible for that provider's safeguards, including its retention and training terms. Pritect's Mistral is then not used for those calls, with fixed exceptions: document OCR, voice transcription, knowledge-base embeddings and, in Speak Up, the report form pre-fill from a voice recording always remain on Pritect's EU-hosted Mistral. There is no silent fallback: if a customer's own provider fails, the call fails rather than rerouting their data.
- European Headquarters
- Stateless Processing
- Zero Data Retention
Core Principles
Human Oversight Required
All AI outputs are advisory only. Every recommendation requires explicit human review and approval before any action is taken. AI augments professional judgment. It never replaces it.
No Training on Your Data
Customer data is never used to train, fine-tune, or improve AI models. Pritect's contract with Mistral includes a training opt-out and Zero Data Retention: your data is processed, the response returned, and nothing is retained by the model provider. AI outputs that Pritect saves, such as Speak Up triage drafts and voice transcripts, stay in your tenant until deleted under its retention schedule.
European AI Infrastructure
Powered by Mistral, a European-headquartered AI provider, included in the platform and serving every organisation by default. AI processing aligns with European data sovereignty principles and EU regulatory expectations. Enterprise customers who prefer a different provider may select one.
No Self-Learning
Pritect's AI does not learn, adapt, or evolve based on usage. No feedback loops, no reinforcement learning, no model drift. Every request is processed independently.
Tenant Isolation & Data Minimisation
Strict tenant-level isolation ensures no cross-contamination between organisations. AI features operate on the minimum data necessary to produce the requested output.
Input Sanitisation & Prompt Protection
All inputs to AI features are sanitised and validated. Prompt injection protections prevent manipulation of AI behaviour through crafted inputs.
AI Clearly Labelled
Every AI-generated output is explicitly labelled as AI-assisted. Users always know when they are viewing AI-generated content versus human-authored information.
EU AI Act Aligned
Pritect's AI features are classified as non-high-risk under the EU AI Act. No biometric identification, emotion recognition, social scoring, or autonomous decision-making.
Detailed AI Governance
Data Processing & Sovereignty
Security & Isolation
Human Oversight & Control
Regulatory Classification & Compliance
Monitoring & Transparency
AI-Powered Capabilities
Pritect integrates AI across governance workflows to accelerate analysis, surface risks, and reduce manual effort, always under human supervision.
- Risk assessment and scoring
- Compliance gap identification
- Regulatory horizon scanning
- Legal obligation triage
- PII detection and classification
- Evidence matching and correlation
- Policy document summarisation
- Board report generation
- Security control recommendations
- Assessment recommendations
- Supplier risk analysis
- Control effectiveness evaluation
Documentation
Access our compliance documentation. Some documents require verification for access.
Publicly available
Master service agreement
Terms and conditions for using Pritect.ai
Implementation services terms
Terms governing onboarding, configuration, and platform consulting
Data processing agreement
Standard DPA for customers processing personal data
Sub-processor list
List of third parties who process data on our behalf
Acceptable use policy
Permitted and prohibited uses of the platform
Third-party licences
Open source software licences and attributions
Privacy notice
How we collect, use, and protect your personal data
Cookie notice
Cookies used on this website and their purposes
Security architecture
Overview of Pritect.ai's security architecture and controls
Penetration test report
Independent white box penetration test of the Pritect.ai platform, May 2026
Request access
ISO/IEC 27001:2022
Information security management system certification
Coming 2026Consensus Assessment Initiative Questionnaire (CAIQ)
Cloud security self-assessment responses
Available on requestFrequently asked questions
Security inquiries
Get in touch
Have security questions or need documentation access? We respond to all inquiries within 2 business days.